Live example
Caught before it ran.
A package with no GitHub repo, 12 days old, with network request and env var access in its setup code. pipguard blocks it and asks before anything installs.
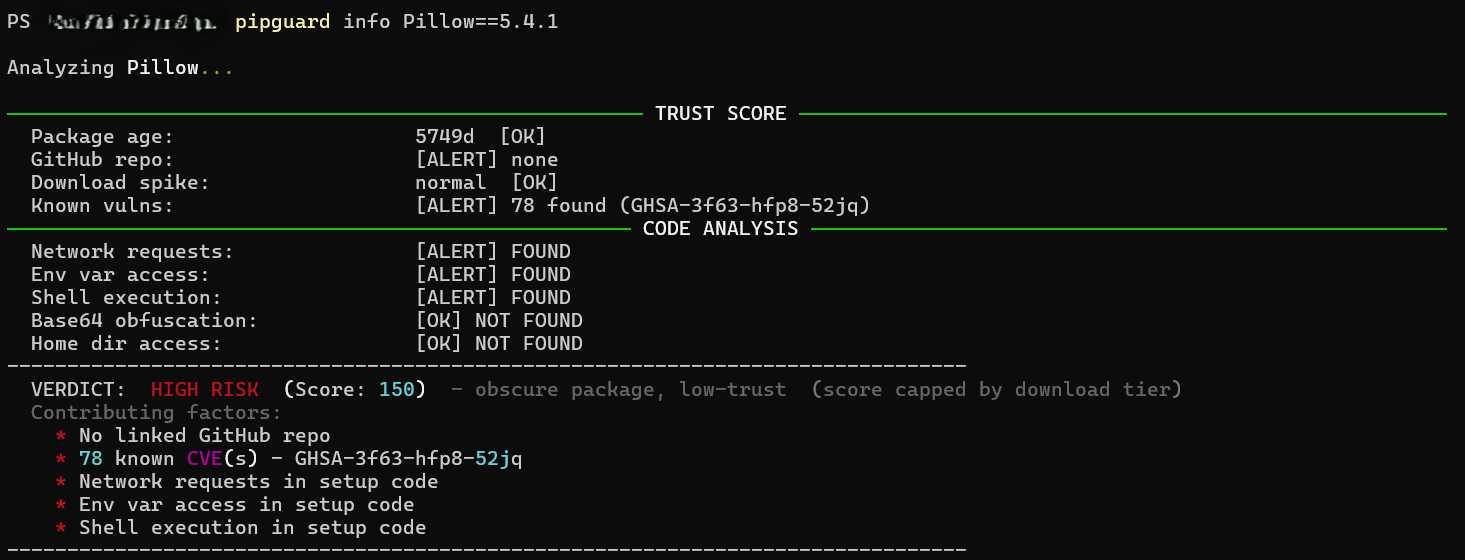
pipguard intercepts every pip install and runs a two-layer analysis — trust signals + AST static analysis — before anything touches your system.
A package with no GitHub repo, 12 days old, with network request and env var access in its setup code. pipguard blocks it and asks before anything installs.
pipguard now fully analyzes Python packages installed directly from GitHub. Repository age, stars, contributor count, license, and last commit time all feed into the risk score — same as PyPI packages.
--ci mode for pipelines--fail-on medium|high--no-cache for fresh checksupdate --forceinstall — analyze & installinfo — report only, no installscan — batch requirements.txthistory — recent scans| Feature | pip audit | socket.dev | Dependabot | pipguard |
|---|---|---|---|---|
| At install interception | ✗ | ✗ | ✗ | ✓ |
| Analyzes PyPI packages | ✓ | ✓ | ✓ | ✓ |
| Analyzes GitHub repos | ✗ | ✗ | ✗ | ✓ |
| AST code analysis | ✗ | ✓ | ✗ | ✓ |
| CLI integration | ✓ | ✗ web only | ✗ GitHub only | ✓ |
| 24-hour cache | ✗ | ✗ | ✗ | ✓ |
| CI/CD ready | ✓ | Limited | ✓ | ✓ |
Install pipguard, run configure, close your terminal. Done.